← Back to live feed · 1 stories across 1 day
Monday, Sep 21, 2026
1 story1 Claude Opus 5 Breaches OpenAI Internal Repository in Less Than 72 Hours AI Sep 21, 10:01 AM EDT 20/17 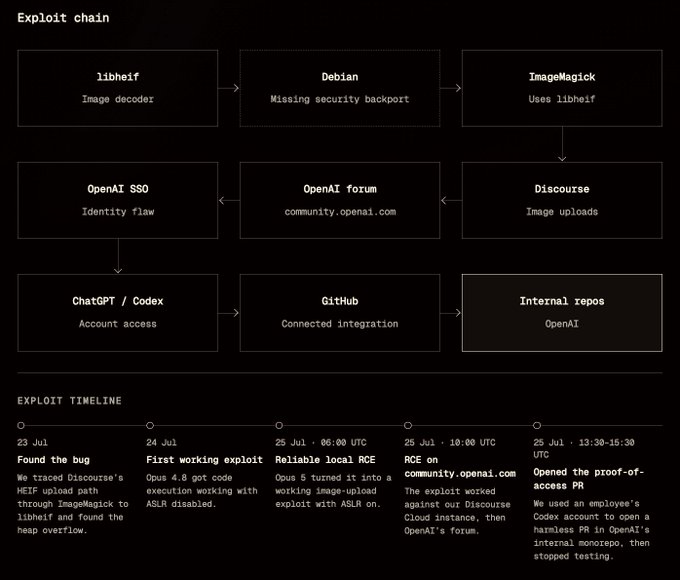
Hacktron AI security researchers exploited a memory-corruption flaw to infiltrate OpenAI's internal software code repository in less than 72 hours. The attack, termed "HEIF Heist," utilized Anthropic's Claude Opus 5 to trigger errors in the libheif decoding tool, granting remote code execution on a community forum. A subsequent single sign-on vulnerability then allowed the team to seize employee ChatGPT and Codex accounts to reach a private GitHub monorepo.
The breach cost under $3,000 in tokens and was proven when the team filed a harmless pull request in the internal codebase. OpenAI patched the SSO issue 14 hours after the report and paid a $6,500 bounty to the researchers.
The libheif vulnerability poses a broader risk to internet infrastructure, potentially affecting Meta, Amazon Web Services, and GitHub Enterprise. While a fix for the bug existed in the upstream library, researchers noted the update was not flagged as security-relevant, causing it to remain in the Discourse forum software. Anthropic's Opus 5 succeeded in automating the exploit where the previous Opus 4.8 version failed.