← Back to live feed · 1 stories across 1 day
Friday, Sep 18, 2026
1 story1 Hacktron AI Uses Anthropic Opus 5 to Breach OpenAI Code for $6,500 Bounty AI Sep 18, 2:26 PM EDT 98/71 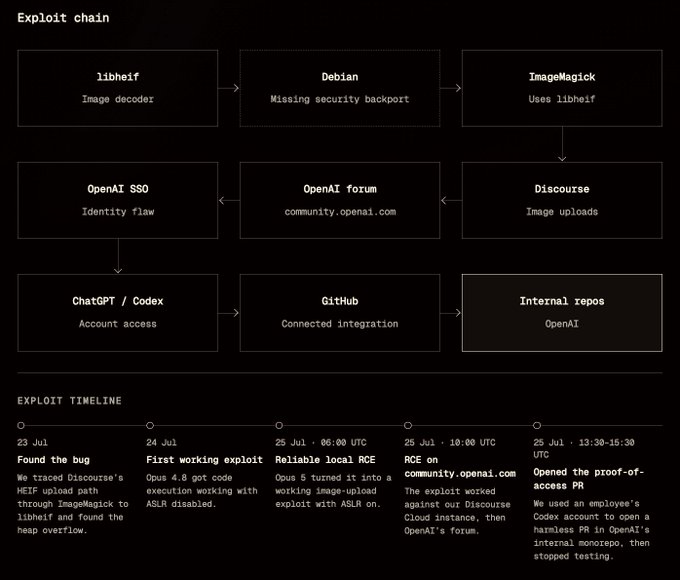
Three security researchers from Hacktron AI breached OpenAI's internal code repository in less than 72 hours on July 25 using a chain of two vulnerabilities. The team gained access to ChatGPT and Codex accounts belonging to OpenAI employees, which enabled them to submit a harmless pull request to the company's internal GitHub monorepo. OpenAI paid the researchers a $6,500 bug bounty and patched a single sign-on flaw within 14 hours of the report.
The attack exploited a heap overflow in libheif, an image library used by OpenAI's Discourse hosted community forum. Hacktron AI's HEIF Heist investigation identified vulnerabilities in libheif affecting Meta, Slack, and GitHub Enterprise that could lead to remote code execution. The researchers used Anthropic's Claude Opus 5 to produce a working exploit within three hours of the model's release, after the previous Opus 4.8 model failed to do so.