← Back to live feed · 1 stories across 1 day
Friday, Sep 18, 2026
1 story1 OpenAI Reassigns 25% of Production Engineers to Security After Claude Opus 5 Breach AI Sep 18, 2:24 AM EDT 74/57 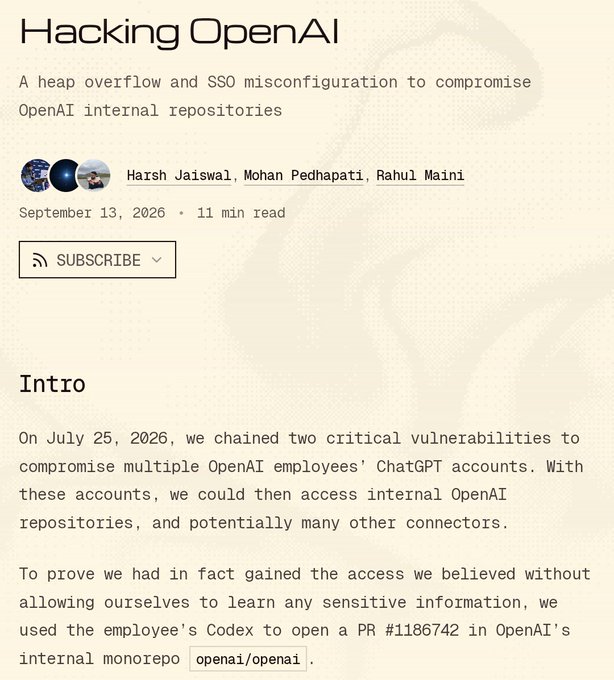
Three security researchers at Hacktron AI exploited a software flaw in an image-processing library to take over OpenAI employee accounts and reach the company's private GitHub monorepo. The team uploaded a HEIF photo to OpenAI's support forum to trigger a bug in the libheif decoder, then used a separate flaw in the company's single sign-on to obtain authentication tokens for ChatGPT and Codex. OpenAI reviewed the incident and found limited reads of private repository metadata and code changes, confirming no model weights were exposed.
The breach was completed in less than 72 hours, with Anthropic's Claude Opus 5 generating a working exploit within three hours of its release after version 4.8 had struggled to refine the attack. OpenAI paid a $6,500 bug bounty and patched the sign-on flaw approximately 14 hours after the report. Following the incident and another AI-assisted breach at Hugging Face, OpenAI temporarily reassigned 25% of its production engineers to security work.