← Back to live feed · 1 stories across 1 day
Saturday, Sep 19, 2026
1 story1 Researchers Use Anthropic’s Claude to Breach OpenAI’s Private Code Repository↩︎ AI Sep 19, 3:05 AM EDT 103/75 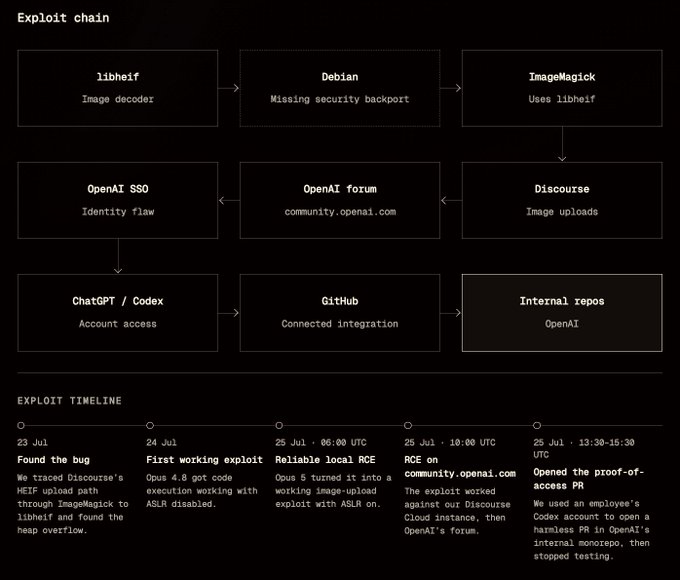
Three researchers at security startup Hacktron AI exploited two flaws to take over OpenAI employee accounts and reach its private GitHub code repository in less than 72 hours. The team used Anthropic’s Claude under OpenAI’s bug bounty program and demonstrated the July 25 breach by submitting a harmless proposed code change through an employee’s Codex account.
The attack began with an image upload that exploited a flaw in libheif, an image processing library used by OpenAI’s Discourse community forum. The library’s developers had already fixed the flaw, but the fix was not flagged as security related and Discourse remained vulnerable. A separate flaw in OpenAI’s login system let the researchers take over ChatGPT and Codex accounts and reach connected services, including GitHub, Slack and Outlook.
The researchers spent less than $3,000 on AI tokens and received a $6,500 bounty from OpenAI. Hacktron said OpenAI fixed the login flaw roughly 14 hours after its report. OpenAI said its review found only “limited reads” of private repository metadata and code changes, and that no model weights were believed exposed.