← Back to live feed · 1 stories across 1 day
Monday, Sep 21, 2026
1 story1 Hacktron AI Researchers Breach OpenAI Internal Code Using Claude Opus 5 AI Sep 21, 10:01 AM EDT 15/13 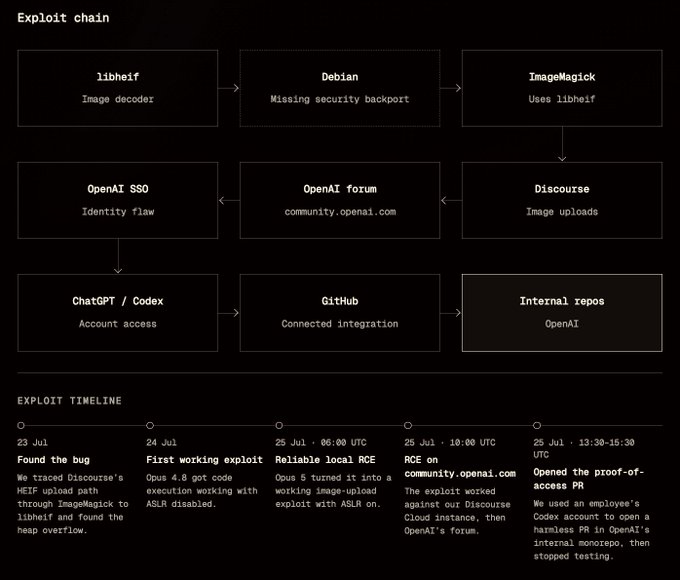
Researchers from Hacktron AI accessed OpenAI's private software repository by exploiting a memory corruption flaw in the libheif image decoding library. The team used Anthropic's Claude Opus 5 to develop the exploit in less than 72 hours for under $3,000 in tokens, bypassing security by uploading a specially crafted HEIF image to a public forum. The attack chain included a single sign-on vulnerability that granted the researchers control over employee Codex accounts and access to the company's internal monorepo.
The HEIF Heist vulnerability extends to other platforms utilizing the same decoding tool, including Meta, Slack, and GitHub Enterprise. OpenAI patched the flaw within 14 hours of the report and paid a $6,500 bug bounty. The researchers provided proof of the breach by submitting a harmless pull request to the internal codebase without downloading any proprietary source code.