← Back to live feed · 1 stories across 1 day
Friday, Sep 18, 2026
1 story1 Researchers Breach OpenAI Internal Code Using Anthropic Opus 5 Model AI Sep 18, 4:29 AM EDT 87/63 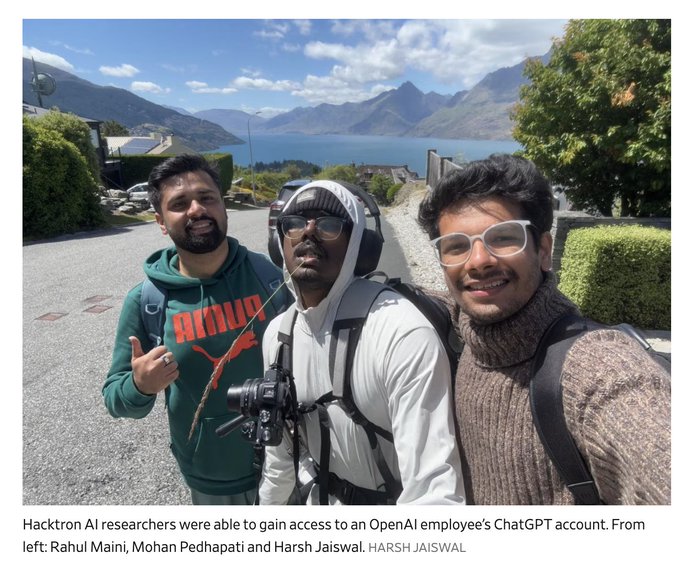
Three independent security researchers from Hacktron AI used a chain of vulnerabilities to gain access to the internal GitHub repository of OpenAI. The team exploited a heap buffer overflow in the libheif image library used by OpenAI's Discourse-hosted support forum to execute remote code. A secondary flaw in the "log in with OpenAI" button then allowed the researchers to hijack employee ChatGPT and Codex accounts to submit a proof-of-concept pull request to the company's internal "monorepo."
Anthropic's Opus 5 model generated the working exploit after the earlier Opus 4.8 version failed. OpenAI patched the login flaw 14 hours after the report and paid a $6,500 bug bounty. Following this breach and a separate incident involving Hugging Face, Greg Brockman stated the company temporarily reassigned 25% of its production engineers to security work. The libheif vulnerability also affected Meta, Slack, and GitHub Enterprise.